Join Veracode’s live webinar to see what the latest GenAI code security data means for your software delivery pipeline, and the practical controls that can make AI-generated code safer.
Among organizations that have adopted AI tools, AI now writes roughly half of all committed code. But across more than 100 models tested since 2023, the average security pass rate is stuck at 56%. Syntax is nearly perfect. Security is not. That’s the headline from Veracode’s 2026 GenAI Code Security Report, and in this live webinar, Chris Wysopal and Jim Manico unpack what the data means for your pipeline and the practical controls that can make AI-generated code safer.
Key Things You Will Learn
- Why a 56% security pass rate changes the risk math for any organization scaling AI-assisted development
- Why the report’s decision to test models without security-specific prompting creates an opening for a different approach
- What intent-based coding actually means: giving AI explicit, framework-specific security requirements before code generation, not after
- How AI-SAST works as a deterministic verification layer for AI-generated code, and why it belongs in your release gate
- What the “Security Token Furnace” costs your team every time AI-generated code isn’t secure the first time, and how to avoid it
- Why “we use the best model” isn’t a security strategy when even the top performer fails nearly one in three security tasks
Speakers:
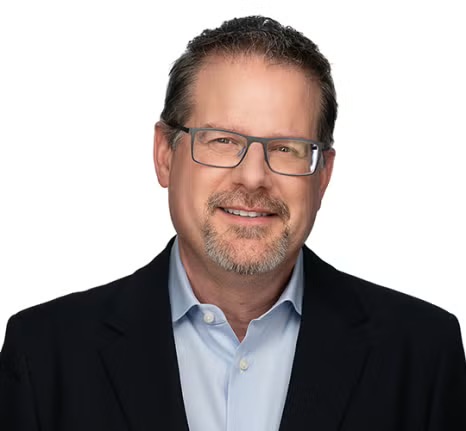
Chris Wysopal
Co-Founder & Chief Security Evangelist
Veracode
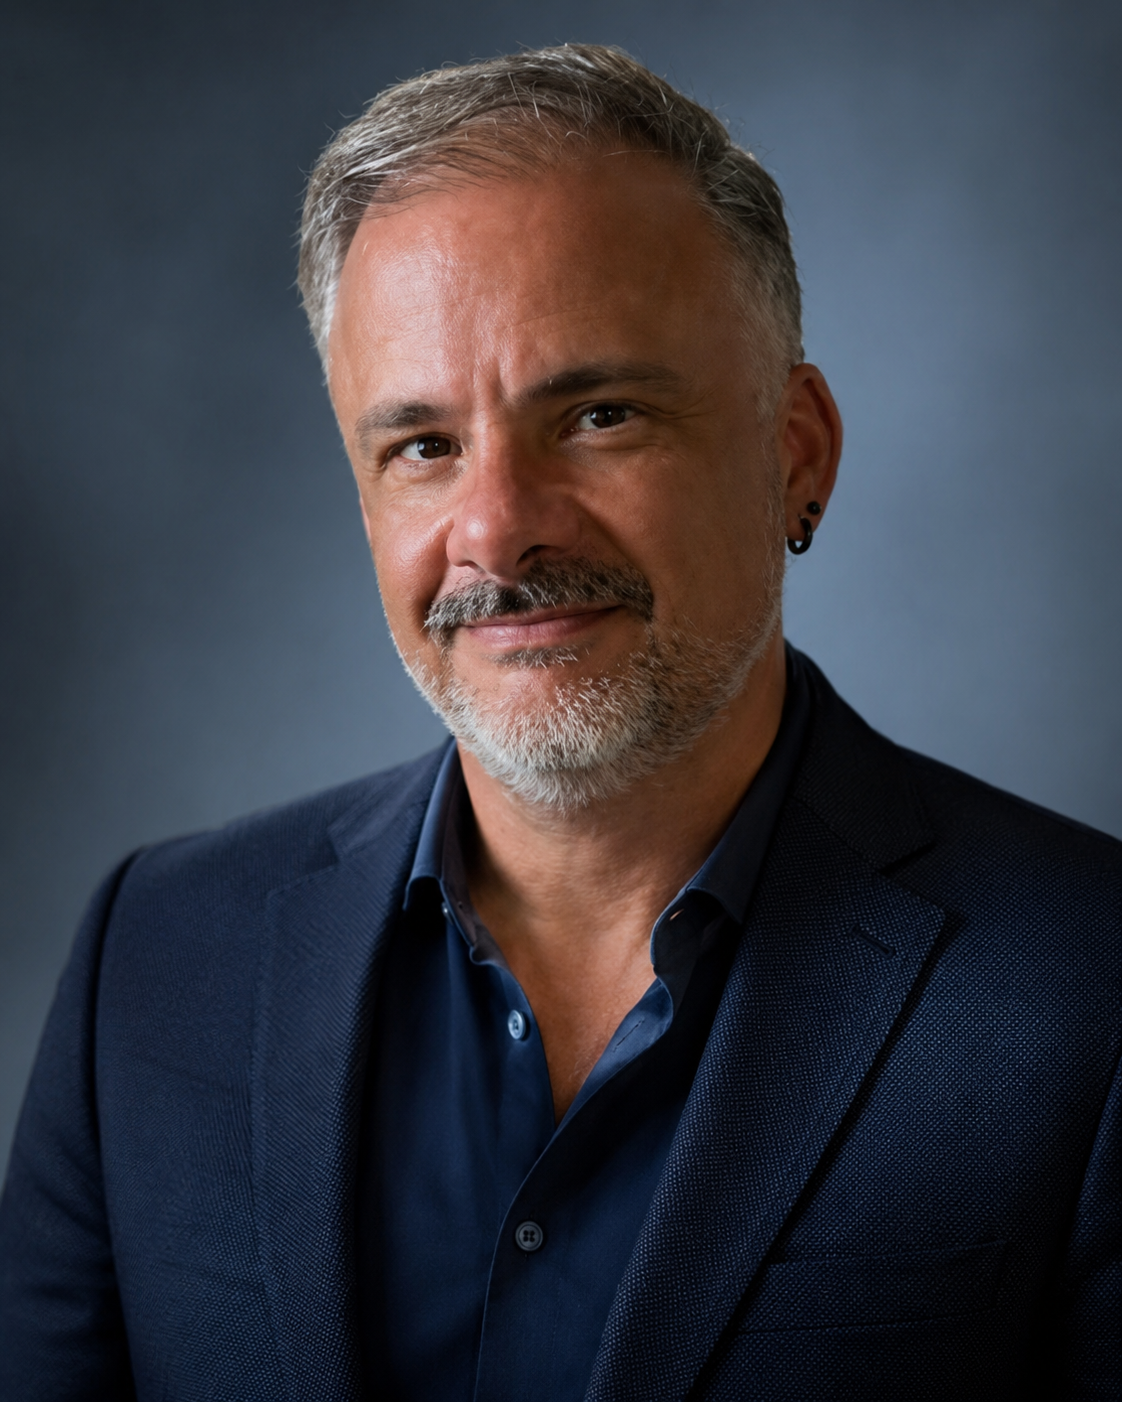
Jim Manico
Founder
Manicode
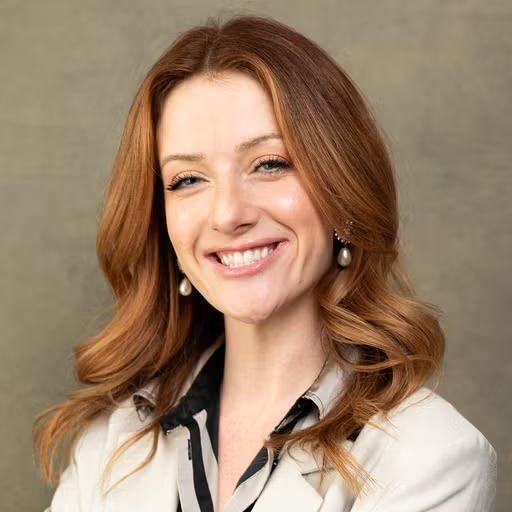
Moderated by Natalie Tischler
Content Marketing Manager
Veracode
Save your seat to hear the findings and the actions security leaders should take now.